
Anti-Malware Allow-List based on Macros

Administrators can now allow-list files from Anti-Malware based on macros they contain.
Some organizations use macros extensively, often including them in the most sensitive and important files for their day to day business.
At times, specific macros are the only way to differentiate between files that should be allow-listed and files that should be inspected for malware.
Harmony Email & Collaboration now allows administrators to allow-list files not only based on their file MD5, but also based on Macros they include.
This new option is available when you choose to create an allow-list for a file that contains at least one macro.
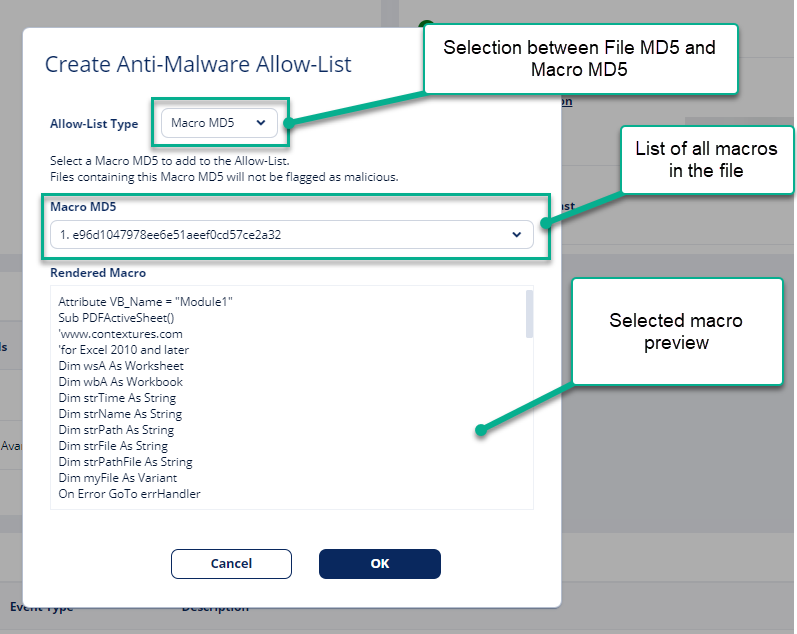
Note – this feature is now gradually deployed and you should see it in your portal within the next 2 weeks.
You may also like

The Inbox Is Disappearing. Why Security Must Follow the Workspace
Enterprise work no longer fits neatly inside a defined perimeter. The modern ...
Check Point Blocks Large-Scale Debt-Relief Email Phishing Campaign Targeting More Than 9,000 Organizations
Check Point has identified and blocked a large-scale email phishing campaign using ...
Attackers Are Turning Microsoft’s Trusted Login System Into Their Latest Phishing Weapon
Attackers are increasingly abandoning fake Microsoft login pages in favor ...
Which Brands Are Impersonated Most? Inside the Q2 2026 Brand Phishing Report
Key Takeaways Microsoft continues to be the single most impersonated ...