State Sponsored Hackers Use Fake Job Offers to Deliver New Zero Day Exploit

It typically begins the same way it has for years, with an approach from a recruiter offering a role at a company the target would recognize, accompanied by a PDF describing the position in convincing detail. That approach remains one of the most effective entry points used by state sponsored threat actors today, and Check Point Research has spent recent months tracking a new wave of it. Operation Dream Job, the long running campaign attributed to the North Korea affiliated Lazarus group, has resurfaced with a previously undisclosed Windows vulnerability (CVE-2026-68820), a newly identified backdoor, and a command and control architecture built almost entirely on infrastructure the group does not own.
Key Takeaways
- Check Point Research uncovered a new wave of a long running, state sponsored campaign that uses fake job offers to target the defense sector, with particular focus on aerospace and aviation organizations in Europe and India
- The attackers used a previously unknown vulnerability in Windows (CVE-2026-68820) to gain full control of infected computers and evade EDR visibility. Check Point reported the issue to Microsoft, which released a fix before this research was published
- Victims are lured through fake recruiter messages and tricked into opening a malicious PDF or installing a trojanized PDF viewer, which quietly installs a newly identified backdoor that gives attackers remote access to the machine
- Rather than running their own servers, the attackers are hijacking legitimate but compromised websites and webmail servers to relay commands, making the malicious traffic harder to distinguish from normal activity
- In at least one case, a real organization that had already been compromised was used to send further phishing messages to new victims, borrowing its reputation to make the campaign more convincing
What is Operation Dream Job and why does it remain effective?
Since early 2026, Check Point Research has tracked a campaign built on a straightforward premise, that professionals in the defense and aerospace sectors will engage with a compelling career opportunity. Posing as recruiters, the threat actor makes contact through platforms such as LinkedIn or direct messaging applications, presents a role at a well known company, and directs the target toward a malicious download. The technique is simple, and it continues to succeed because it targets professional ambition via sophisticated social engineering.
How does the attack unfold?
Check Point Research identified two infection chains operating in parallel.
The first relies on DLL sideloading. Victims are directed to download an encrypted archive containing a legitimate, digitally signed PDF viewer, a malicious DLL, and an encrypted payload disguised as a PDF file. When the executable is launched, the malicious DLL displays a decoy job description to the victim while decrypting and executing MISTPEN in memory, a lightweight downloader first documented by Mandiant in 2024 that communicates with attacker infrastructure through the Microsoft Graph API and OneDrive. Once reconnaissance and persistence modules have run their course and the AFD.sys exploit has succeeded, MISTPEN deploys ForestTiger, a well documented Lazarus backdoor that provides the attackers with long term remote access to the host.
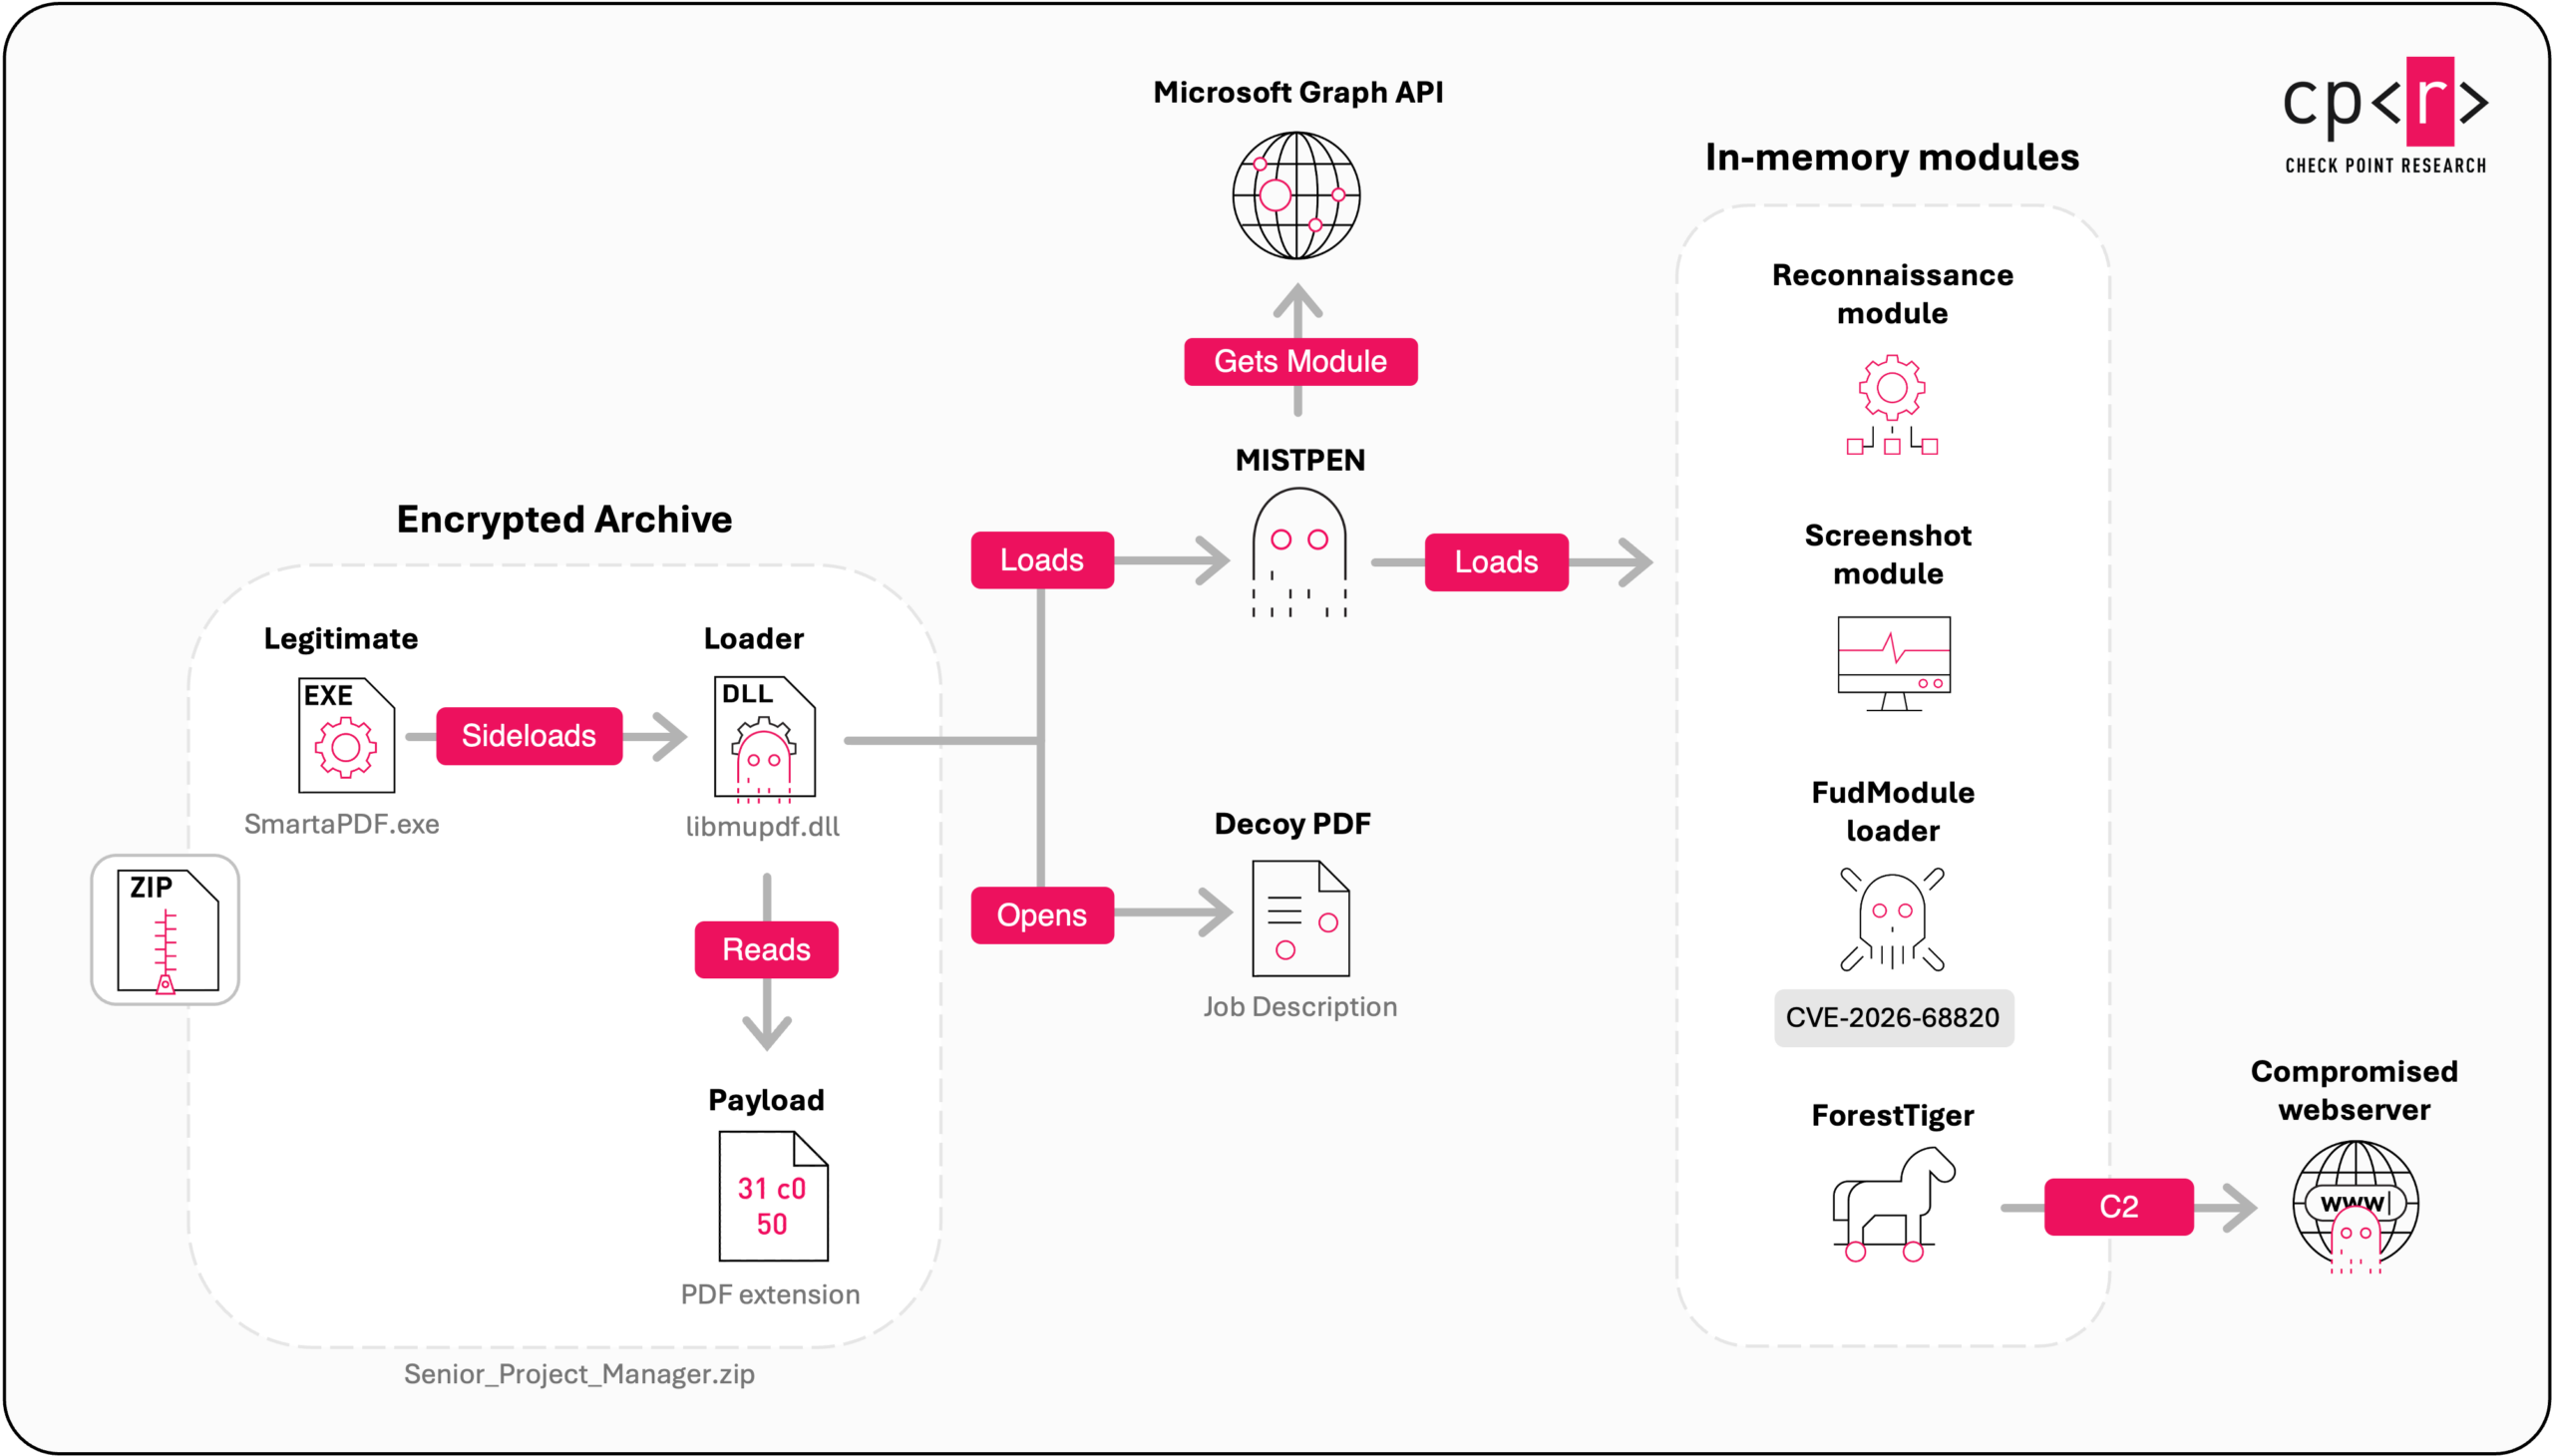
Figure 1 – High-level overview of the DLL sideloading infection chain
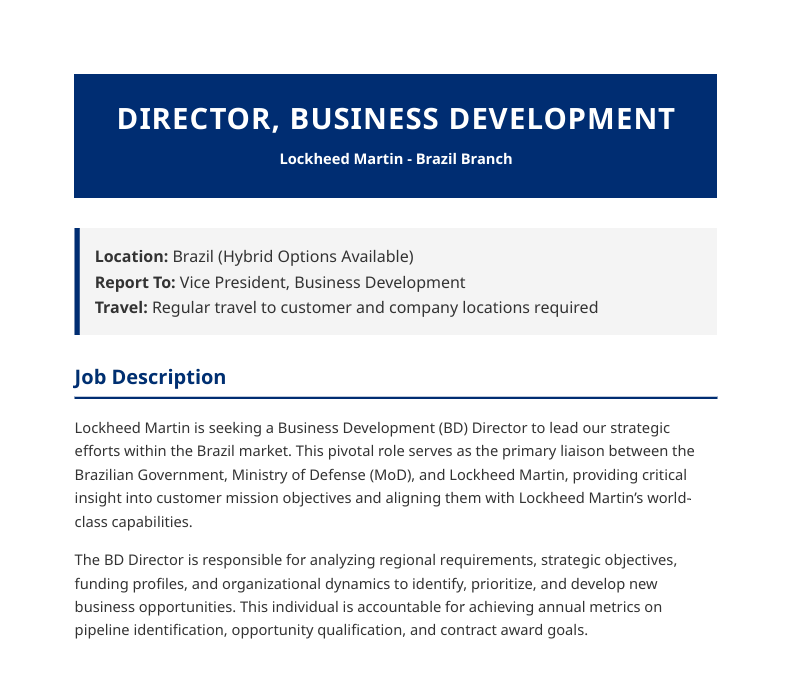
Figure 2 – PDF decoy impersonating Lockheed Martin job description
The second chain is more recent and shares several characteristics with a campaign described by ESET against the UAV sector in 2025. Victims are instructed to download SecurityPDF, a trojanized PDF viewer, from one of several websites impersonating Enveil, a legitimate privacy technology company with no actual connection to the attack. Once installed, the modified viewer inspects any PDF opened through it for a hidden marker. When the marker is present, the application decrypts and launches an embedded payload that loads the Troy backdoor directly into memory.
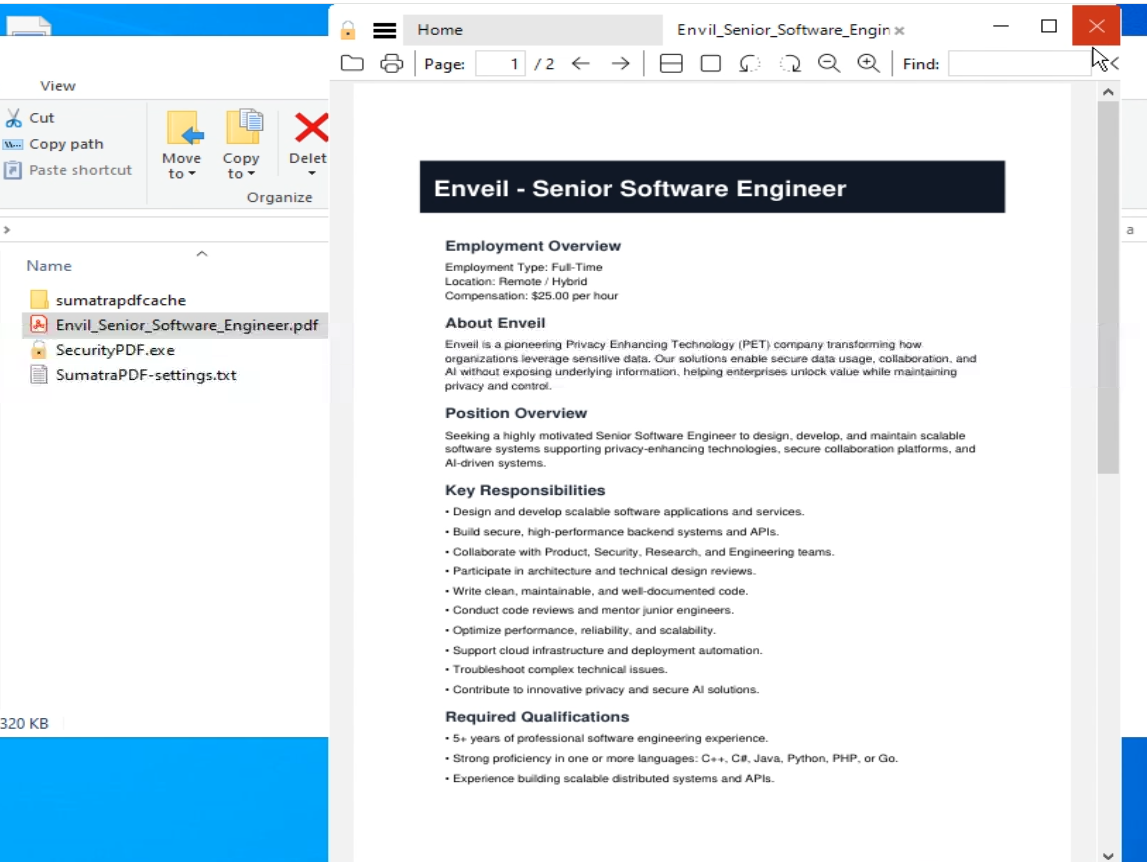
Figure 3 – Crafted PDF opened by SecurityPDF
What is the zero day, and why does it matter?
Once installed, the malware quietly gathers information about the infected computer before deploying its most serious capability, an exploit that takes advantage of a flaw in a core Windows component responsible for network connections. At first, the flaw resembled CVE-2025-60719, an unrelated vulnerability in the same component that Microsoft had already fixed in November 2025, but testing against a fully updated Windows 11 system confirmed this was something new. In practical terms, the flaw allows an attacker who has already gotten malware onto a machine to escalate from limited access to complete control of it, the kind of control normally reserved for the operating system itself.
That level of access is then used to run a highly capable rootkit, a tool designed to hide the attacker’s presence from security software and disable the logging systems that would otherwise reveal what’s happening on the machine. This version, which Check Point Research designates v3.1, builds on a tool previously reported by Gen Digital in 2024, and adds a new capability that lets it tamper with a Windows feature designed to verify that running software is trustworthy.
Check Point Research reported the vulnerability to Microsoft on July 28, 2026. Microsoft confirmed the issue three days later, assigned it CVE-2026-68820 on August 5, and released a fix on August 11 as part of Patch Tuesday.
What does the Troy backdoor do?
Troy is a previously undocumented, single DLL implant with a notably broad capability set for its size. It supports seventeen operator commands spanning file enumeration, upload and download, archive and exfiltration operations, interactive shell access, process termination, in memory DLL injection, and configuration updates, delivered through a consistent tasking and response framework. Its name derives from a PDB path embedded in the compiled binary, a path Check Point Research has observed in earlier Lazarus samples, including one referenced in an ESET report published last year.
Why is command and control running through compromised websites?
Rather than operating dedicated servers, Lazarus is increasingly relying on compromised Roundcube webmail installations and content management system platforms, many vulnerable to CVE-2025-49113, together with credentials obtained from dark web leaks. These servers are infected with RelayShell, a previously undocumented PHP webshell that functions less like a conventional backdoor and more as a communication relay between infected endpoints and the operator, exchanging commands and responses through simple text files. Check Point Research identified at least seventeen unique server identifiers associated with this relay network, and observed the operators connecting through commercial VPN services to further obscure their location.
Who is being targeted, and what should organizations do?
The current campaign concentrates on defense, aerospace, and aviation organizations, with confirmed activity in Europe, Asia and South America including France, Germany, Brazil, and India. Given the combination of a zero day vulnerability that now have a patch, a new modular backdoor, and web based infrastructure designed to resemble legitimate traffic, security teams in these sectors should prioritize the August Patch Tuesday update, review the indicators of compromise published in Check Point Research publication, and apply the same level of scrutiny to unsolicited recruiting outreach that they would apply to any unverified download request.
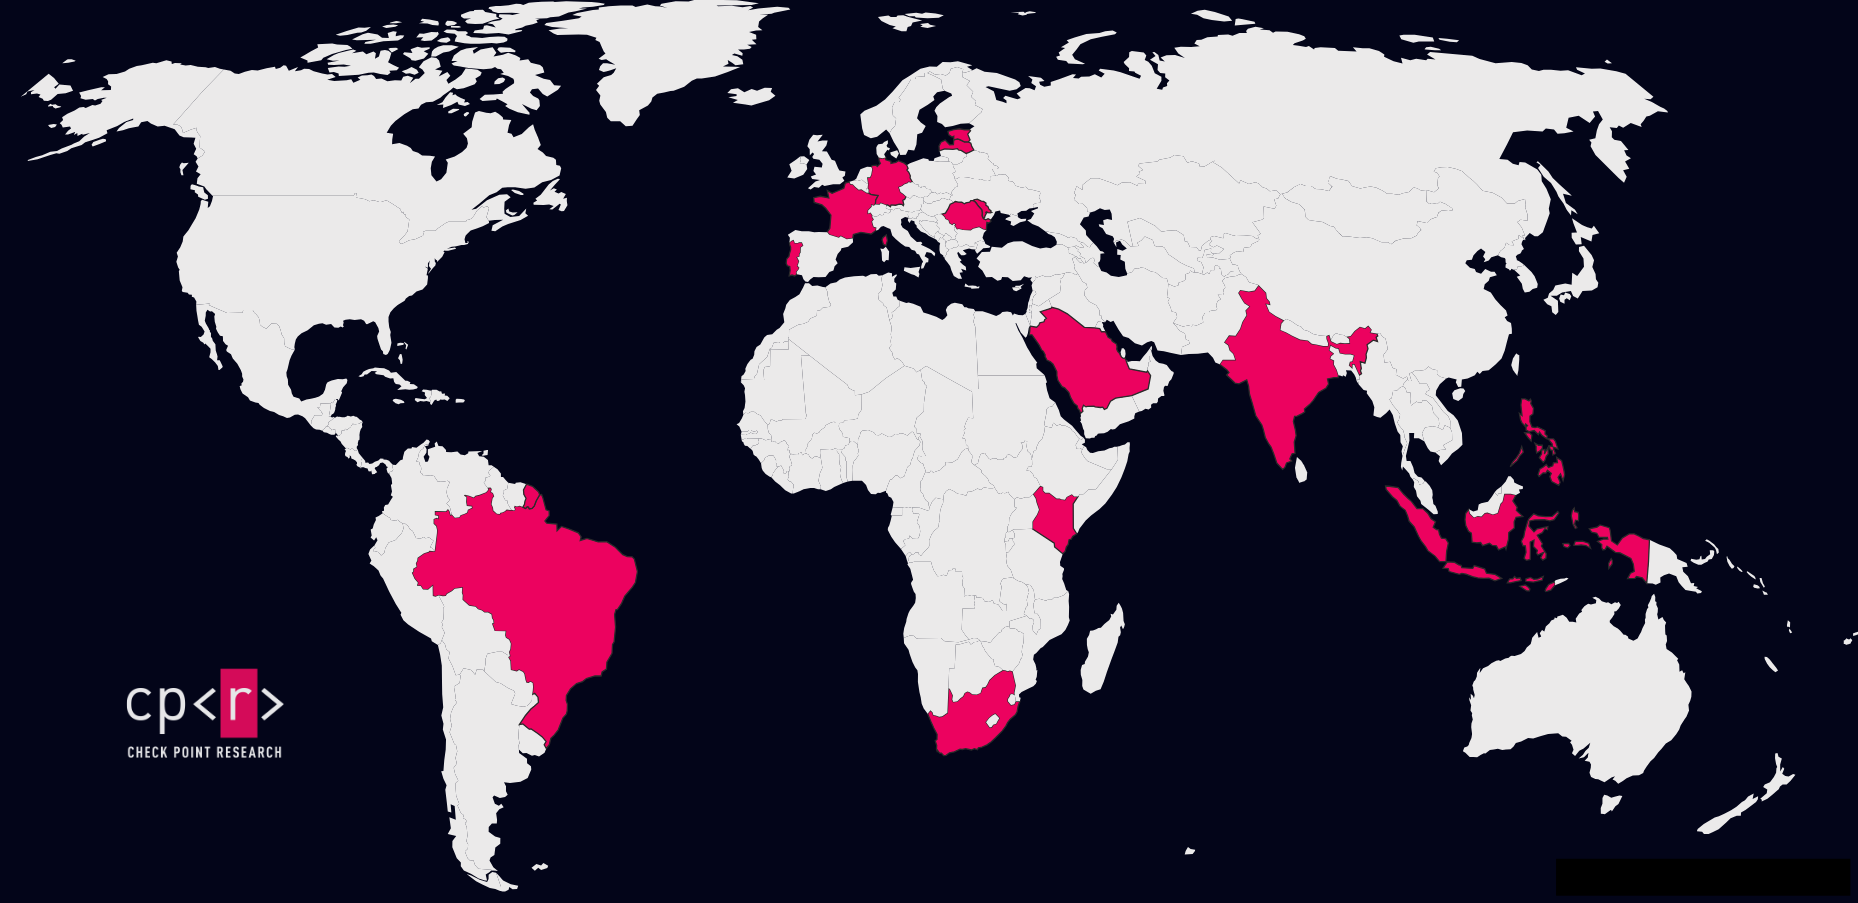
Figure 4 – Lazarus Operation Dream Job Global Campaign Targets
How can organizations defend against this kind of attack?
Nearly every stage of this campaign plays out on the endpoint itself rather than in transit, which makes endpoint level prevention the most relevant line of defense. Check Point Endpoint Security is built to address this attack chain at several points. Threat Emulation and Threat Extraction analyze incoming files, including archives and PDFs of the kind used in both infection chains, before they reach the user, and can strip or sandbox active content before it executes. Behavioral Guard is designed to identify malware that avoids writing to disk, the same in memory approach used by MISTPEN and the Troy backdoor throughout this campaign. Against the AFD.sys vulnerability specifically, the Anti Exploit component is built to detect zero day and unknown exploitation attempts against vulnerable processes, which is the layer most relevant to a kernel level privilege escalation of this kind, independent of whether a signature for the specific technique exists yet. Organizations in the defense, aerospace, and aviation sectors, the primary targets of this campaign, should treat endpoint prevention of this type as a priority alongside patching CVE-2026-68820 directly.
There is a second, easily overlooked angle to this campaign worth addressing directly, the risk of becoming the compromised infrastructure rather than the intended target. The Roundcube and CMS servers used to run RelayShell were not breached with anything exotic, just credentials already leaked on the dark web, paired with a known, unpatched vulnerability sitting on a public-facing server. Check Point Exposure Management flags and fixes both of these. It’s dark web monitoring surfaces an organization’s leaked credentials, and it’s attack surface visibility shows which internet-facing systems, like a Roundcube server, are exposed and overdue for a patch, or a virtual patch until one is released. Then these risks are safely and quickly remediated. For any organization running public-facing webmail or CMS infrastructure, seeing both at once is key to avoiding becoming a relay node in a campaign like this one.
For the full report, access the Check Point Research publication here.
You may also like
Gambling Goblin: A Chinese-Speaking Actor Hijacks Brazilian Government Sites to Fuel a Global SEO Fraud Machine
Back-to-School Cyber Risks Surge as Education Remains the World’s Most Attacked Sector

The Mistake That Exposed a Global Cyber Crime Operation