


A zero day flaw in a trusted supply chain software turned a legitimate government collaboration tool into a malware delivery platform.
Operation TrueChaos at a Glance
- Zero day vulnerability discovered in the TrueConf client update mechanism (CVE20263502, CVSS 7.8)
- In the wild exploitation observed against government entities in Southeast Asia
- Malware delivery via legitimate software updates, requiring no phishing or additional initial compromise vectors
- Havoc, a powerful post exploitation framework, used as the suspected final stage payload
- Victimology, tooling, and infrastructure suggest ties to a Chinese-nexus threat actor (moderate confidence)
- Check Point Research were discovered the use of this vulnerability in the wild and responsibly notified the vendor who released a fix; the fix is included in the TrueConf Windows client starting with version 8.5.3, which was released in March 2026. The current version of the desktop apps is 8.5.2.
At the start of 2026, Check Point Research uncovered a targeted cyber espionage campaign that challenges long held assumptions about trust inside enterprise and government networks. Dubbed Operation TrueChaos, the campaign did not rely on phishing, stolen credentials, or exploitation of internet facing servers. Instead, attackers abused a previously unknown zero day vulnerability in a trusted, widely deployed enterprise videoconferencing platform to quietly distribute malware across multiple government agencies at once.
The vulnerability, tracked as CVE 2026 3502, impacted the TrueConf Windows client, a collaboration platform used extensively by government, defense, critical infrastructure organizations and reputable businesses such as banks due to its on premises, offline capable architecture. By exploiting weaknesses in TrueConf’s update validation process, attackers were able to weaponize the software’s trusted update mechanism, transforming it into a supply chain style malware delivery channel.
This research highlights a sophisticated pattern in modern cyber operations: attackers increasingly target the invisible trust relationships inside secure environments, rather than attempting to break in from the outside.
Inside CVE 2026 3502: How a Trusted Update Became a Malware Delivery System
TrueConf is not consumer software. It is designed specifically for secure, separated, and sovereign environments, allowing government agencies to communicate without internet connectivity. This makes it particularly attractive for ministries, defense institutions, and critical infrastructure operators.
In Operation TrueChaos, the attackers gained control of a central on premises TrueConf server, operated by a government IT organization, and replaced a legitimate client update with a malicious one. Every connected agency that trusted that server automatically became vulnerable.
This approach offers attackers extraordinary scale and stealth:
- No suspicious external downloads
- No malicious links
- No security warnings for users
- Malware delivered as a “legitimate update”
Once installed, the malicious update quietly deployed tools that enabled reconnaissance, persistence, privilege escalation, and communication with attacker controlled command and control servers – without alerting the victim.

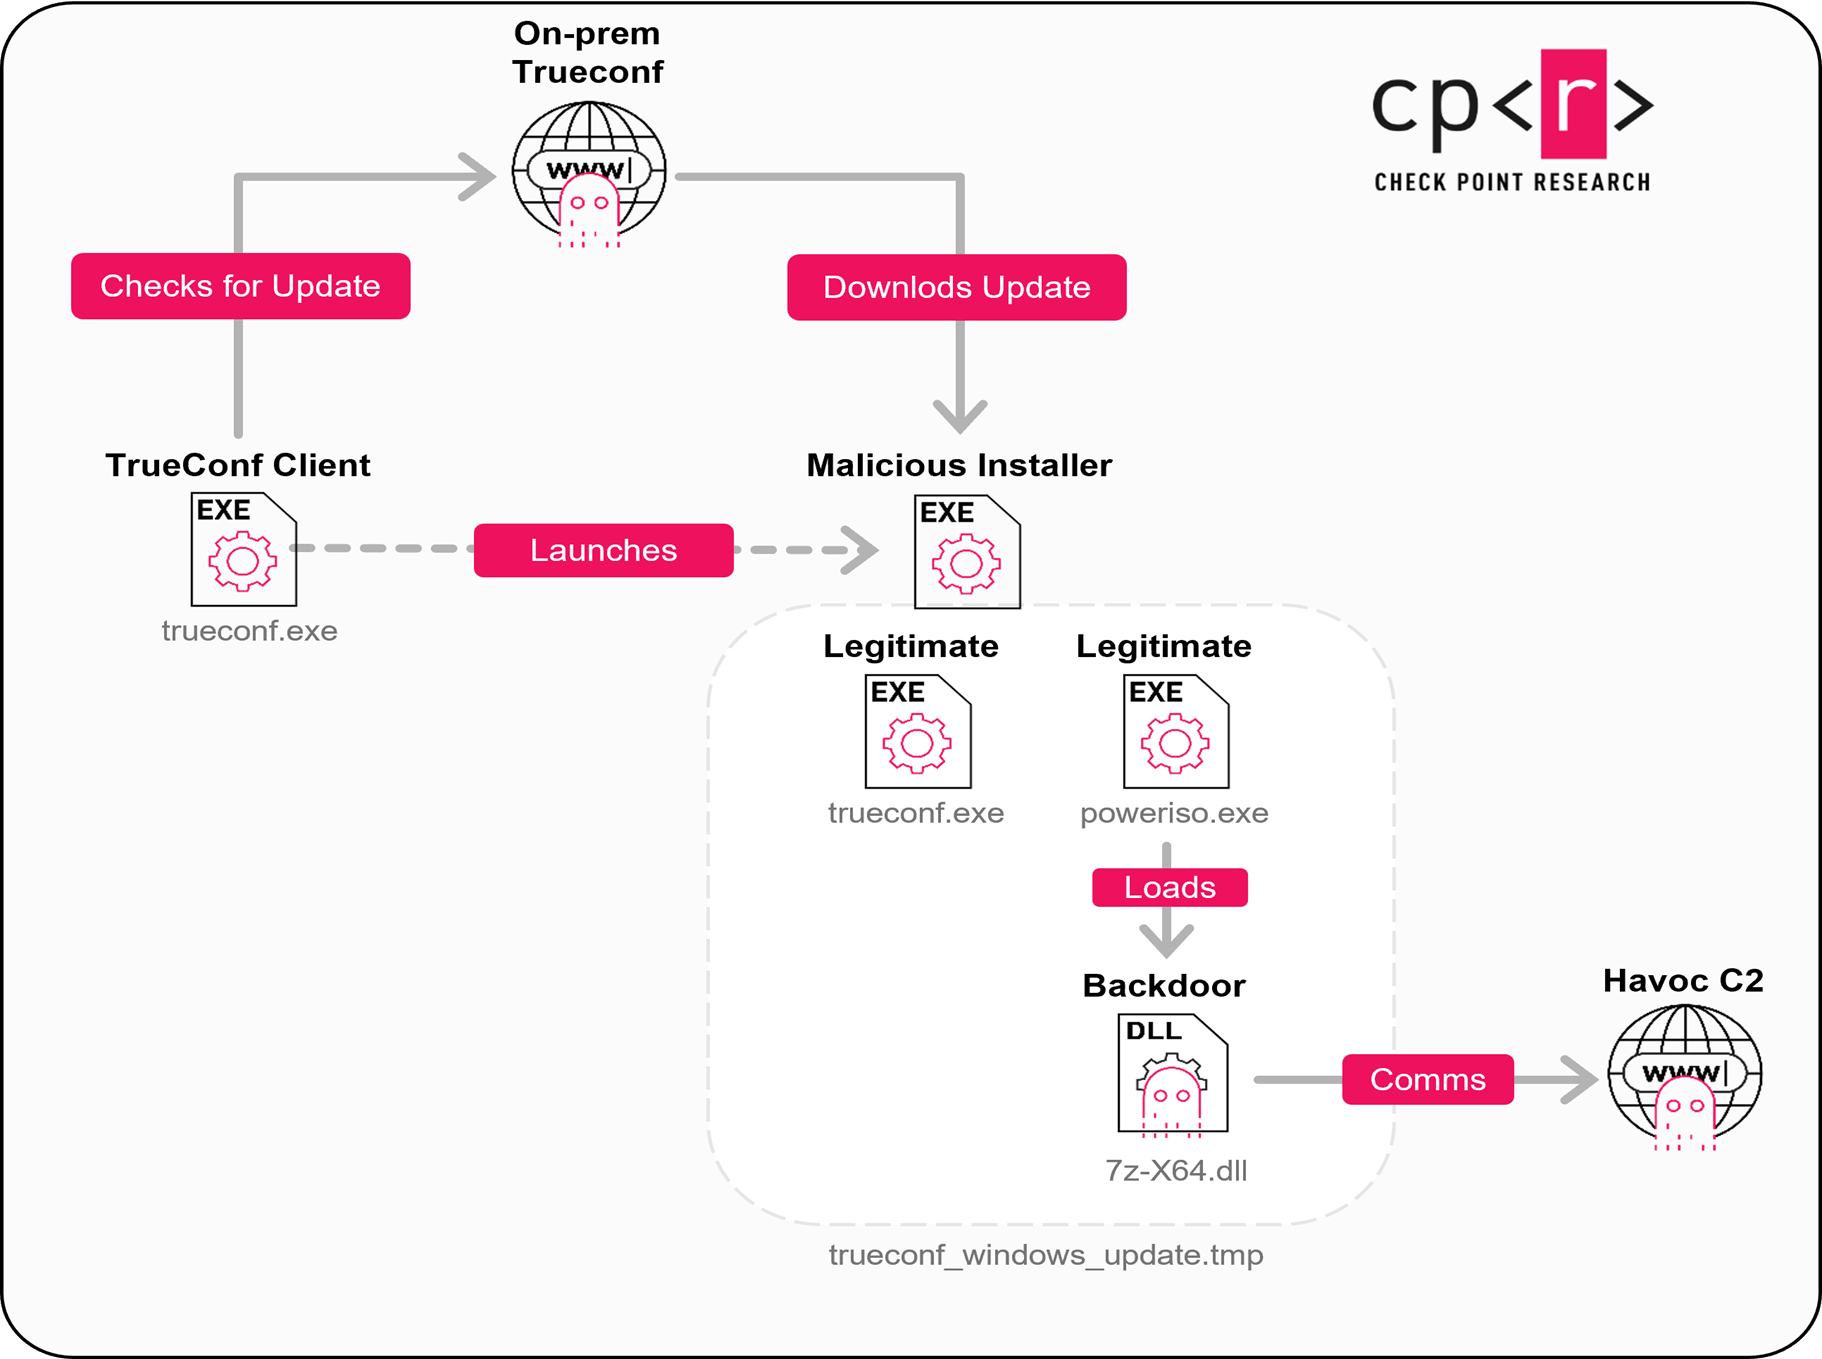
Malicious Client Update Attack Chain
At the heart of Operation TrueChaos is a flaw in how the TrueConf Windows client validated software updates delivered from an on premises server. In secure enterprise and government environments, update mechanisms are often implicitly trusted, particularly when they operate entirely within a private network. That trust became the attacker’s entry point.
When a TrueConf client starts, it automatically checks its connected on premises server for newer versions. If the server advertises a newer client build, the user is prompted to download and install the update directly from the internal server. Critically, researchers found that the client did not sufficiently verify the integrity or authenticity of the update package before execution.
This meant that:
- Any executable placed on the TrueConf server could be presented as a “legitimate update”
- The client would download and execute it without robust cryptographic validation
- The update inherited the full trust of an enterprise application
As the attack chain leveraged a legitimate application, trusted internal update workflow and User approved installation prompts, the initial infection blended seamlessly into normal enterprise activity. Most notably, the attacker did not need to compromise each endpoint individually. Every device connected to the compromised server, and trusting it for updates, became a potential infection point. What is usually considered a strength of centralized management became a force multiplier for the attacker.
The malicious update was carefully constructed:
- It performed a valid client upgrade to avoid suspicion
- It dropped additional files that abused DLL sideloading to execute attacker controlled code
- This code enabled reconnaissance, privilege escalation, persistence, and communication with attacker command and control infrastructure
This vulnerability has since been fixed, with TrueConf introducing improved validation controls in updated client versions. However, the incident underscores a broader challenge: software update mechanisms themselves have become high value targets for advanced attackers.
The Role of Zero Day Vulnerabilities in Modern Espionage
Zero day vulnerabilities, flaws unknown to vendors and defenders, remain one of the most powerful tools in advanced cyber operations. What makes CVE20263502 particularly significant is where it sits in the attack chain.
Rather than exploiting browsers or operating systems, this flaw targeted a trusted internal software update process – a mechanism most organizations implicitly rely on and rarely monitor.
This marks a broader industry issue: as organizations harden their perimeters, attackers increasingly target software supply chains, management tools, and internal trust relationships – especially in environments assumed to be “secure by design.”
Why This Campaign Looks Like Cyber Nation State-Backed Espionage
Several indicators suggest Operation TrueChaos was motivated by intelligence collection rather than financial gain:
- Target selection focused on government and government affiliated entities
- Use of Havoc, an advanced post exploitation framework which is also associated with state aligned operations
- Command and control infrastructure hosted in environments previously linked to Chinese-nexus threat activity
- Overlap in targeting with other Chinese-linked malware frameworks, including ShadowPad
Industry Impact: What Operation TrueChaos Signals
Operation TrueChaos exposes a blind spot across many organizations, not just those using TrueConf.
What this means for the industry in summary is:
- “Trusted” internal tools can be abused at scale
- On premises are not inherently immune to advanced threats
- Software update mechanisms are now high value attack targets
- Zero days increasingly enable supply chain style attacks without third party compromise
How to Stay Safe: Reducing Zero Day and Supply Chain Risk
While zero day vulnerabilities cannot always be prevented, their impact can be significantly reduced. Organizations – especially governments and critical infrastructure operators – should take the following steps immediately:
- Patch and Update
- Ensure TrueConf Windows clients are updated to version 8.5.3 or later, which includes the vendor’s fix for CVE20263502
- Monitor Internal Update Channels
- Monitor for unexpected executables, unsigned binaries, or anomalous update behavior
- Harden Privileged Infrastructure
- Restrict administrative access to central servers that distribute software or configuration updates
- Apply least privilege controls and multifactor authentication wherever possible
- Detect Lateral Trust Abuse
- Look for endpoint activity originating from legitimate internal applications behaving abnormally
- Hunt for suspicious process chains, DLL sideloading behavior, and unsigned update files
- Assume Breach—Even in Secure Environments
- Zero trust principles apply inside the network, not just at the perimeter
- Validate, verify, and continuously monitor – even systems designed to operate offline
Operation TrueChaos is more than a single zero day disclosure – it is a warning. As attackers continue to evolve, trust itself has become the attack surface. Collaboration tools, management servers, and update mechanisms now sit squarely in the crosshairs of advanced threat actors.
For governments and enterprises alike, the lesson is clear: Security isn’t just about blocking access – it’s about continuously validating what you already trust.
Staying ahead of today’s threats means securing not only endpoints and networks, but also the invisible systems that bind them together.
Read the full research report here.